Financial institutions are rapidly integrating external AI and Large Language Model (LLM) platforms to drive operational efficiency. However, connecting core banking infrastructure to third-party AI models introduces unprecedented attack vectors, prompt injection risks, and data leakage vulnerabilities.
With the latest press release on ServiceNow Operational Resilience AI threat response, technology leaders can now establish complete visibility, automated guardrails, and real-time containment over external AI interactions. In this article, we examine how to secure your enterprise AI ecosystem without stalling innovation.Get a Free ServiceNow AI Threat & Resilience Assessment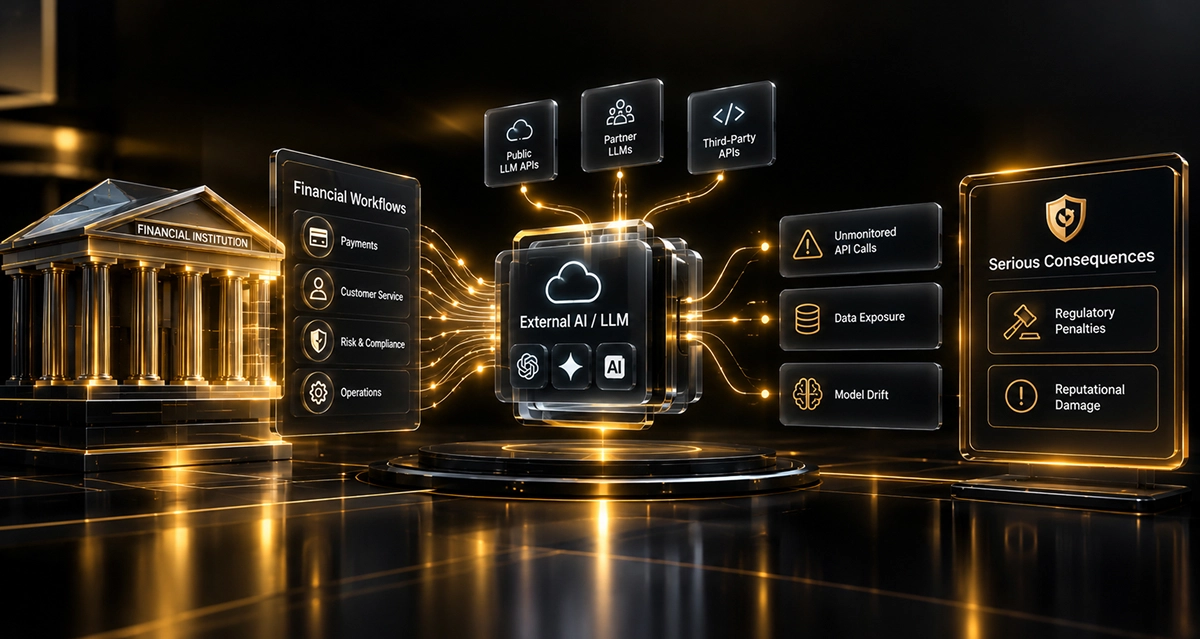
Connecting financial workflows to public or partner LLM APIs accelerates service delivery, but it expands your threat surface exponentially. Without centralized logging, security teams remain blind to unmonitored API calls, proprietary data exposure, and model drift across departments.
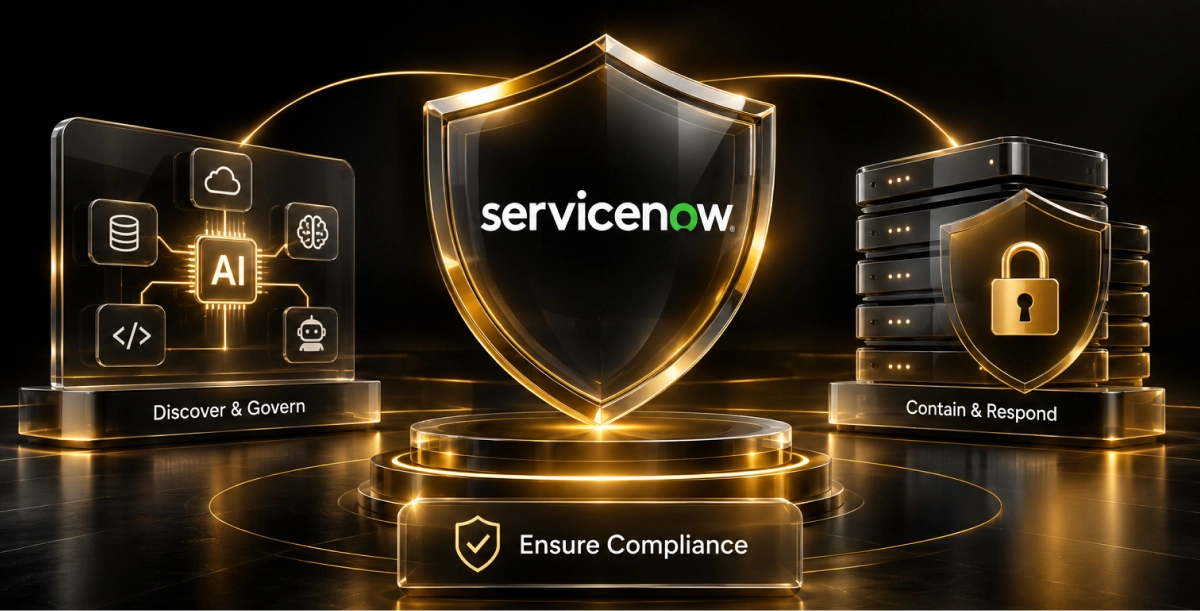
Standard security tools fail to monitor the nuanced logic of AI interactions. When an external LLM experiences a hallucination or security exploit, financial institutions face immediate regulatory penalties and severe reputational damage under global operational resilience mandates.The ServiceNow Operational Resilience solution acts as a centralized control plane, bridging risk management with automated threat response across your technology stack:
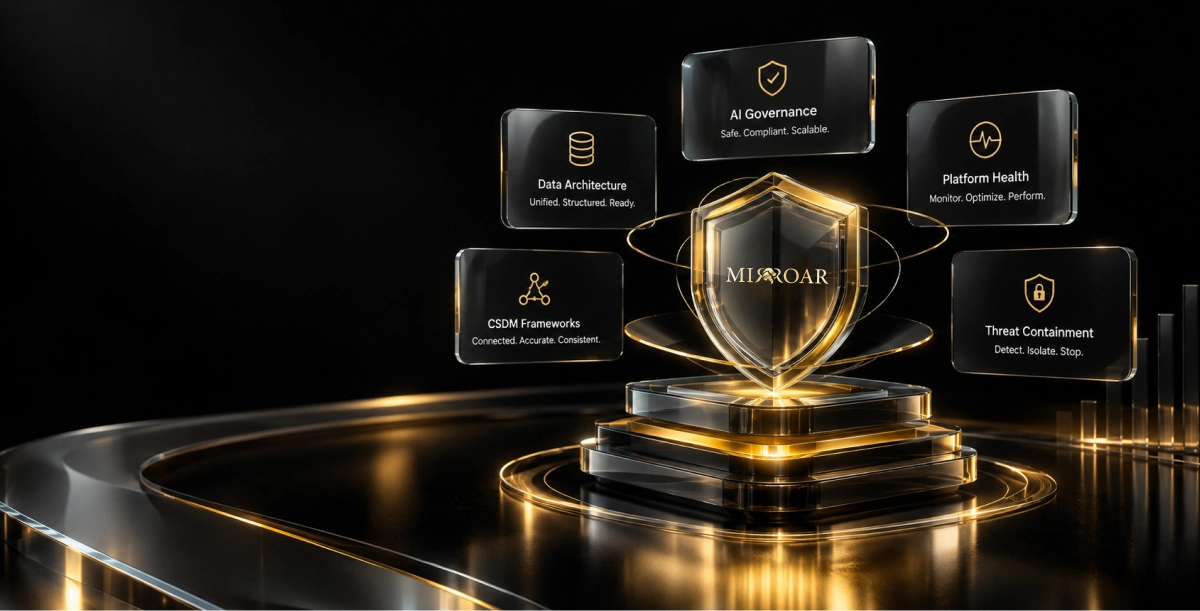
Mirroar positions strict governance, data architecture, and platform health at the core of every deployment. By refining CSDM frameworks and establishing automated threat containment workflows, Mirroar helps financial institutions adopt advanced AI capabilities safely, eliminating technical debt while establishing scalable platform governance.
Mirroar provides end-to-end consulting, seamless implementation, and proactive managed services to streamline your operational resilience deployment. Our certified architects conduct comprehensive instance health audits, configure isolated developer sandboxes, and align platform releases with strict ServiceNow best practices to maximize platform ROI.Integrating external LLMs into financial operations brings immense competitive advantage, but it requires uncompromised governance. Deploying ServiceNow Operational Resilience with Mirroar ensures your enterprise detects, contains, and neutralizes AI threats in real time.
Talk to a Mirroar ServiceNow Platform Architect Today


